Contact UsDMCA policyAbout UsPrivacy PolicyTerms of UseDisclaimerCookie Policy
Trending

This Mac malware breaks through Apple's defenses — what you need to do
This Mac malware breaks through Apple's defenses — what you need to do

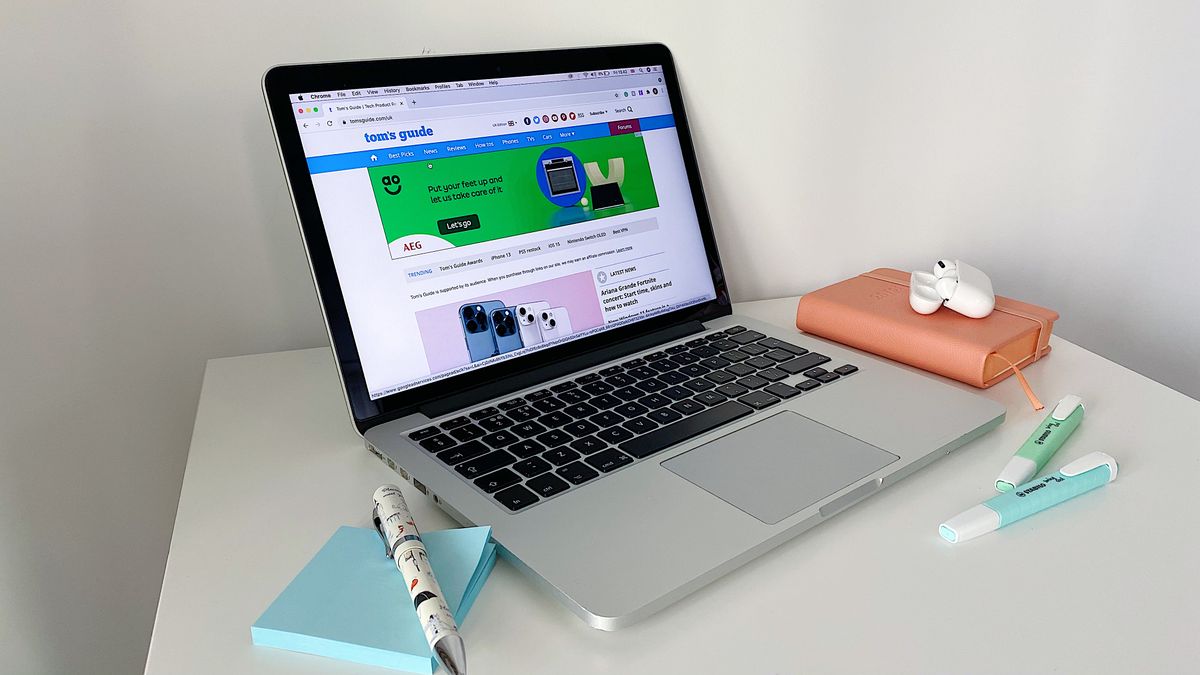
It’s baaack. A notorious form of Mac malware called AdLoad, first spotted in 2017, has returned and is blitzing through macOS’ built-in defenses, reports security firm Sentinel One.

Sentinel One says that since November of last year, it’s seen more than 150 new strains of AdLoad, with “a sharp uptick throughout July and in particular the early weeks of August 2021.” 

They also dodge Apple’s XProtect malware scanner, because many of the AdLoad strains don’t match the malware profiles in XProtect’s database. Some are also “notarized” to get past Apple’s newest layer of defenses. 

“The fact that hundreds of unique samples of a well-known adware variant have been circulating for at least 10 months and yet still remain undetected by Apple’s built-in malware scanner demonstrates the necessity of adding further endpoint security controls to Mac devices,” says Sentinel One.

What you can do to protect yourself

You’re going to need one of the best Mac antivirus programs to stop this one, as Apple’s own protections often won’t be enough.
You could, in theory, prevent an AdLoad infection by refusing to provide your admin password when the malware begins the installation process. 

But like most Mac malware, it will try to fool you into authorizing its installation by pretending your password is needed for some other reason. For example, an earlier Sentinel One report notes that AdLoad installers often masquerade as Adobe Flash Player installers.

How AdLoad works

AdLoad makes money by redirecting your web traffic. It takes over your browser’s search-engine results and points them to sites that may pay AdLoad’s creators a fee, and also injects its own set of ads on top of legitimate web ads.

That’s not the worst kind of malware infection to have, but AdLoad also burrows into the operating system to make sure it’s difficult to remove. And if this kind of middleweight Mac malware makes it on to your machine, who knows what kind of more serious infections you could also have?

“The good news for those without additional security protection is that the previous variant we reported in 2019 is now detected by XProtect,” says Sentinel One’s newer report. “The bad news is the variant used in this new campaign is undetected by any of those rules.”

Apple has been revoking the developer certificates as soon as it spots an AdLoad strain, but “we see new samples signed with fresh certificates appearing within a matter of hours and days,” says the report.

“Truly, it is a game of whack-a-mole.”

This story was earlier reported by Bleeping Computer.

Stay connected with us on social media platform for instant update click here to join our Twitter, & Facebook

We are now on Telegram. Click here to join our channel (@TechiUpdate) and stay updated with the latest Technology headlines.

For all the latest Technology News Click Here 

 For the latest news and updates, follow us on Google News. 

Read original article here

Denial of responsibility! TechAzi is an automatic aggregator around the global media. All the content are available free on Internet. We have just arranged it in one platform for educational purpose only. In each content, the hyperlink to the primary source is specified. All trademarks belong to their rightful owners, all materials to their authors. If you are the owner of the content and do not want us to publish your materials on our website, please contact us by email – [email protected]. The content will be deleted within 24 hours.

CategoryTechnology

Related News